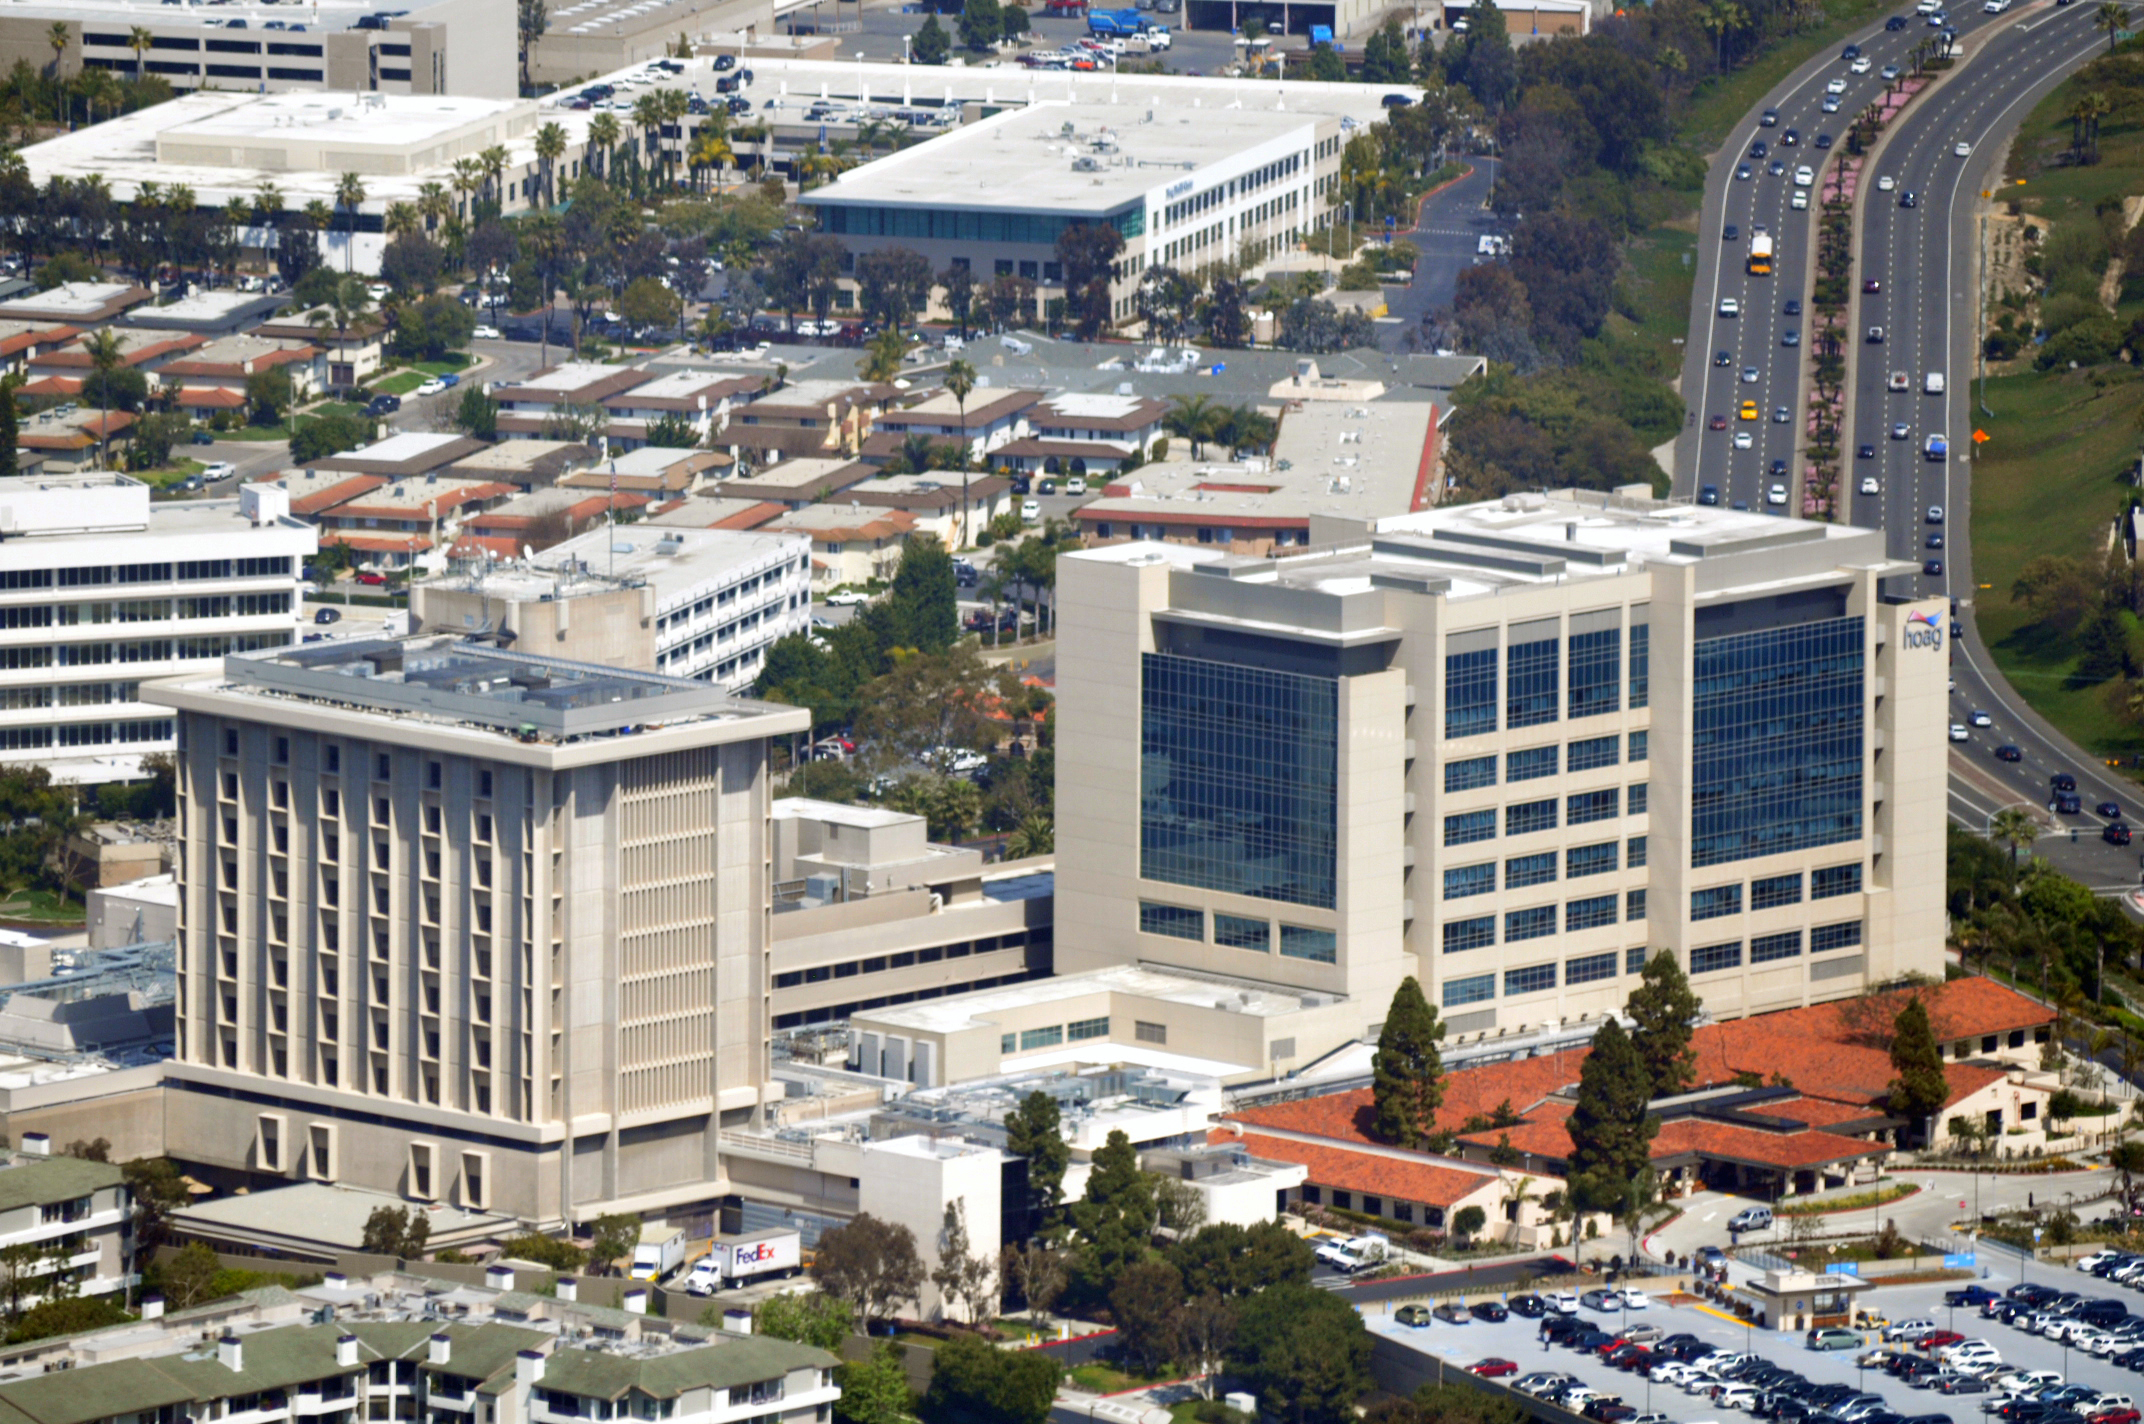
Hoag Memorial Hospital Presbyterian says patient data may have been exposed after the hospital system detected suspicious network activity on Oct. 8.
Hoag filed a notice with the California Attorney General's office on Nov. 4, as reported by Becker's Hospital Review. The notification tells patients that files on Hoag's network "may have been accessed without authorization."
What it does not say: how many patients are affected, what caused the incident, or which Hoag locations had data in the compromised files.
Hoag operates acute care hospitals in Newport Beach and Irvine along with clinics and urgent care centers across Orange County, according to Medical Daily. The notice does not specify whether patients at all sites, or only some, could be affected.
What Hoag has disclosed
The hospital said it brought in independent forensic experts after discovering the Oct. 8 activity. An independent review team determined on Oct. 25 that some patients' personal or protected health information may have been in the affected data, according to the AG filing.
The publicly available notification letters list names as one category of potentially exposed information. Additional data categories appear as placeholders in the public filing, according to Becker's Hospital Review. Individual letters sent to patients may contain more detail about their own records.
The notice was signed by Kimberlee Rosa, Hoag's vice president and chief compliance and integrity officer.
Free identity protection offered
Hoag is offering affected patients free identity protection services through IDX, a data breach response company. The specific services vary by individual, but may include dark web monitoring, credit monitoring, a $1,000,000 insurance reimbursement policy and identity theft recovery assistance, according to the AG filing.
Patients can enroll by calling 1-877-201-3399 or visiting IDX online. Representatives are available Monday through Friday, 6 a.m. to 6 p.m. Pacific Time.
The enrollment deadline is Feb. 4, 2027.
What remains unknown
Four key details are still missing from the public record: the number of affected patients, the specific types of data exposed beyond names, the cause of the network activity and the dates when data may have been accessed.
Hoag said in the notice that it took steps to secure its network and added security measures after the discovery. The hospital has not reported any disruption to its hospitals or appointments, according to Medical Daily.
Under HIPAA, covered health care organizations generally must notify affected individuals without unreasonable delay and within 60 days after discovering a breach of unsecured protected health information. Breaches affecting 500 or more individuals must also be reported to HHS within that timeframe; smaller breaches may be reported annually. HHS maintains a public listing of larger breaches.